NinjaOne Extends Browser Management To Give MSPs More Visibility, Control
‘Up until now, they’ve been left blind to these things. Now we’ve given them the visibility to understand what’s going on and the control to protect their end users and customers,’ says Matt Hastings, SVP of product management at NinjaOne.
NinjaOne is extending its Unified IT Operations Platform into the browser with the launch of NinjaOne Browser Management, helping MSPs better secure customer environments without forcing employees to change the browsers they already use.
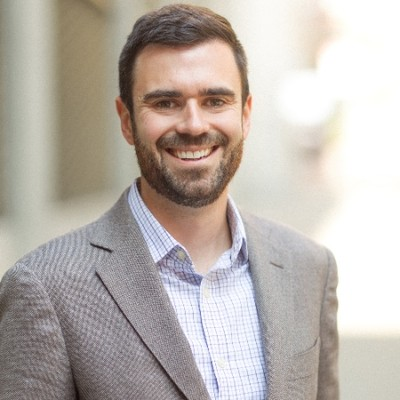
SaaS applications, AI tools and browser extensions have increasingly replaced traditional installed software, according to NinjaOne’s Matt Hastings (pictured above), creating new opportunities for productivity but also new security risks. Malicious browser extensions can potentially access sensitive information without triggering traditional endpoint or network security controls.
“It gives them the governance of the browser,” Hastings, SVP of product management at NinjaOne, told CRN. “This just extends it into that application layer of those browsers, better securing end users from installing malicious extensions and ultimately just providing a better, safer environment.”
[Related: NinjaOne Didn’t Need $400M, But Investors Came Knocking Anyway]
The product gives MSPs a live inventory of browser extensions and versions, visibility into website activity, risk scores to flag potentially dangerous extensions and centralized policies to approve or block extensions, control configurations and restrict URL access.
Hastings sees that as an opportunity for MSPs to turn an emerging risk into a customer-facing service.
“The last thing you want is for a user to expose information, so this just gives them another tool in their arsenal to go out and supply service and supply value to their customers,” he said.
Erickson Dental Technologies’ Lars Andersland said the rollout did not require end users to change their habits or move to a new browser, allowing him to add visibility and control without creating disruption.
“Now we have a live view of what’s actually running across every employee's browser and can act before something becomes a real problem,” Andersland, a service technician at Eagan, Minnesota-based Erickson, told CRN in an email. “That directly translates into fewer security incidents and lower risk for our clients.”
By meeting users where they already work, the product makes it easier for MSPs to support customers without forcing day-to-day behavior changes, Hastings said.
The AI piece may be where that browser control becomes even more critical. As employees increasingly access generative AI through extensions and web-based chat tools, Hastings said Ninja’s roadmap includes deeper capabilities to help MSPs monitor and govern that activity from the browser itself.
For NinjaOne, the bigger play is turning browser management into a customer-facing service MSPs can use to cut risk, improve cyber hygiene and protect one of the most exposed layers of modern work.
“Up until now, they’ve been left blind to these things,” Hastings said. “Now we’ve given them the visibility to understand what’s going on and the control to protect their end users and customers.”