MSPs On Customers Rushing To Deploy AI: ‘It’s Like A Kid In A Candy Store’
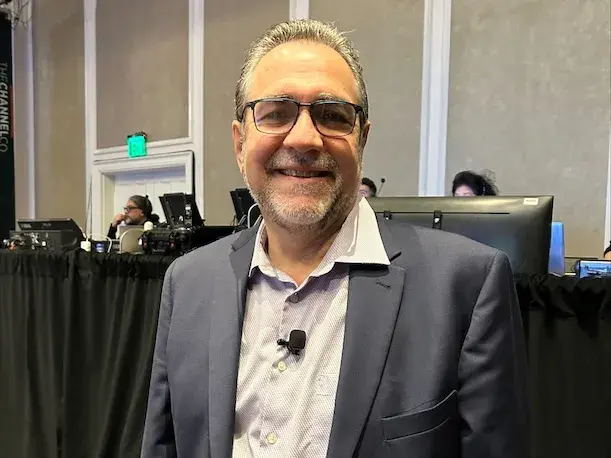
‘[Customers] are very anxious about getting that AI out there. When we talk about the readiness assessment, it’s a hard sale. They just want it. They don’t care about the ramifications,’ says Michael Goldstein, market president of Southeast Florida at MSP Entech.
MSPs are struggling to keep pace with customers rushing to adopt AI, as employees introduce AI tools into IT environments without understanding the data security and governance risks involved.
The challenge, some MSPs told CRN, isn’t getting customers interested in AI. It’s getting them to understand that deploying the technology without proper permissions, visibility and security controls can expose sensitive data.
Michael Goldstein, market president of Southeast Florida at Fort Myers, Fla.-based Entech, said his customers are so eager to get AI into their business that conversations about readiness and risk become more and more difficult.
[Related: 9 MSP Execs On AI Usage Concerns In 2026]
“They are very anxious about getting that AI out there,” Goldstein told CRN. “When we talk about the readiness assessment, it’s a hard sale. They just want it. They don’t care about the ramifications. It’s like a kid in a candy store.”
And he added that AI security requires executive-level involvement, not just technical safeguards implemented by an MSP.
“This usually is not a technical issue. It’s a management issue,” he said. “Executives have to understand what they’re getting into and what their exposure is. Technically, we can roll out everything, but you need management to understand the risks.”
At Austin, Texas-based GSC Technologies, cloud security analyst Brenda Scott said the first step in an AI engagement is determining what employees are already using.
“In a lot of tenants, it shows employees already using several AI tools before the business has decided anything about AI,” Scott told CRN. “And it isn’t just websites. We find desktop apps, Office add-ins and browser apps too.”
GSC then takes stock of which platforms employees are accessing, how they’re using them and what information is being entered into those tools.
“The biggest concern is confidential information like client data, financials or internal documents being pasted into a tool the company doesn’t control,” Scott said, adding that governance cannot be a one-time conversation. “AI tools keep changing, new ones show up in forms we didn’t have to block a year ago, and more people are using them every month. So we keep revisiting it with clients as their usage grows.”
Stanley Louissaint, founder and president of Watchung, N.J.-based MSP Fluid Designs, said he’s seeing customers make AI adoption decisions before involving his MSP, leaving him to address problems after deployment.
“Clients are not coming to us and asking us about our opinion on AI. Clients are coming to us and telling us what they’re implementing,” Louissaint told CRN.
He said his team typically hears from customers only after they encounter roadblocks, including permission problems and other technical issues. Rather than refusing deployments, the approach is to explain the risks, recommend appropriate safeguards and let the customer ultimately decide how to proceed.
“We have taken the position that we will not be a roadblock to our clients and what they want to do,” he said. “If you want to do something, we’re going to give you all of the risks associated with it. We’re going to tell you what you should be doing. But then, ultimately, it’s up to you.”
He attributed part of the problem to how easily employees can access AI tools without involving their MSP.
“You can sign up for ChatGPT in all of 30 seconds and tie in your Google account,” he said. “There’s nothing stopping them from doing that.”
What MSPs are seeing is also reflected in the latest findings from U.K.-based Inforcer’s latest MSP Microsoft Readiness Report, which surveyed 406 MSPs globally.
The research found that 76 percent of MSPs said customers ask about AI at least monthly, while 47 percent field AI questions weekly. Yet only 14 percent said they have full visibility into the AI tools their customers use. Another 63 percent reported only partial visibility.
And the governance gap is apparent in Microsoft Copilot deployments. Inforcer found that 56 percent of customer tenants paying for Copilot have neither data loss prevention policies nor sensitivity labels enabled. Just 16 percent have both protections.
Will Connor, co-founder of Inforcer, said the biggest surprise was how quickly MSPs have embraced AI delivery without establishing the data governance foundation needed to support it.
“People are already delivering AI, but they haven’t caught up,” Connor told CRN. “They’ve got the AI in first before they’ve really got their hands around the data.”
He said MSPs typically helped customers migrate files into SharePoint without addressing permissions and access controls. AI changes that as Copilot can dig up information employees don’t always have permission to access.
“All of a sudden everybody in the organization has access to the payroll run or the redundancy list or whatever may not have been properly permissioned or labeled,” he said.
The report also found that 62 percent of MSPs offer Copilot readiness services, compared with 46 percent offering Purview or data protection services. Another 41 percent identified data hygiene as the most commonly cited obstacle to Copilot deployment.
“If you don’t secure the data layer, there’s going to be likely issues with the AI rollout in general,” he said. “Delivering something like an AI readiness exercise before you go and sell the licensing of the AI would actually set MSPs up for a lot more success.”